-

SECURITY HUB
Secure your business
Understand risks. Prevent attacks. Safeguard your data.
Strong security. Strong business.
Welcome to Deutsche Bank’s Security Hub for corporate clients - your central resource for practical guidance on protecting your organization, employees and sensitive information from cyber threats.
Cybercrime is no longer a distant threat, it affects companies of every size, in every industry and region.
Cyber incidents are now ranked as one of the top business risks worldwide, ahead of many other threats such as market developments or natural disasters. Hundreds of serious incidents are reported in Europe each year across the financial sector and its corporate clients.
Key numbers on cybercrime
*Source: bitsfrombytes.com, August 6th 2026
$ 10.8
trillion
Projected global costs of cybercrime in 2026*
$ 4.44
million
Average global data breach cost*
44
percent
Ransomware in all breaches*
$ 5.08
million
Average ransomware incident total cost*
Managing cyber risks
Running a business today entails more than daily operations, it also means managing complex security risks.
From protecting sensitive data and digital infrastructure, to maintaining employee awareness of ever-changing threats - in business, information security is paramount. Customer data, financial records and intellectual property are attractive targets for criminals. In a recent global risk survey, companies named data breaches as the cyber threat they fear most.
For organizations, the impact goes far beyond the immediate cost of an incident:
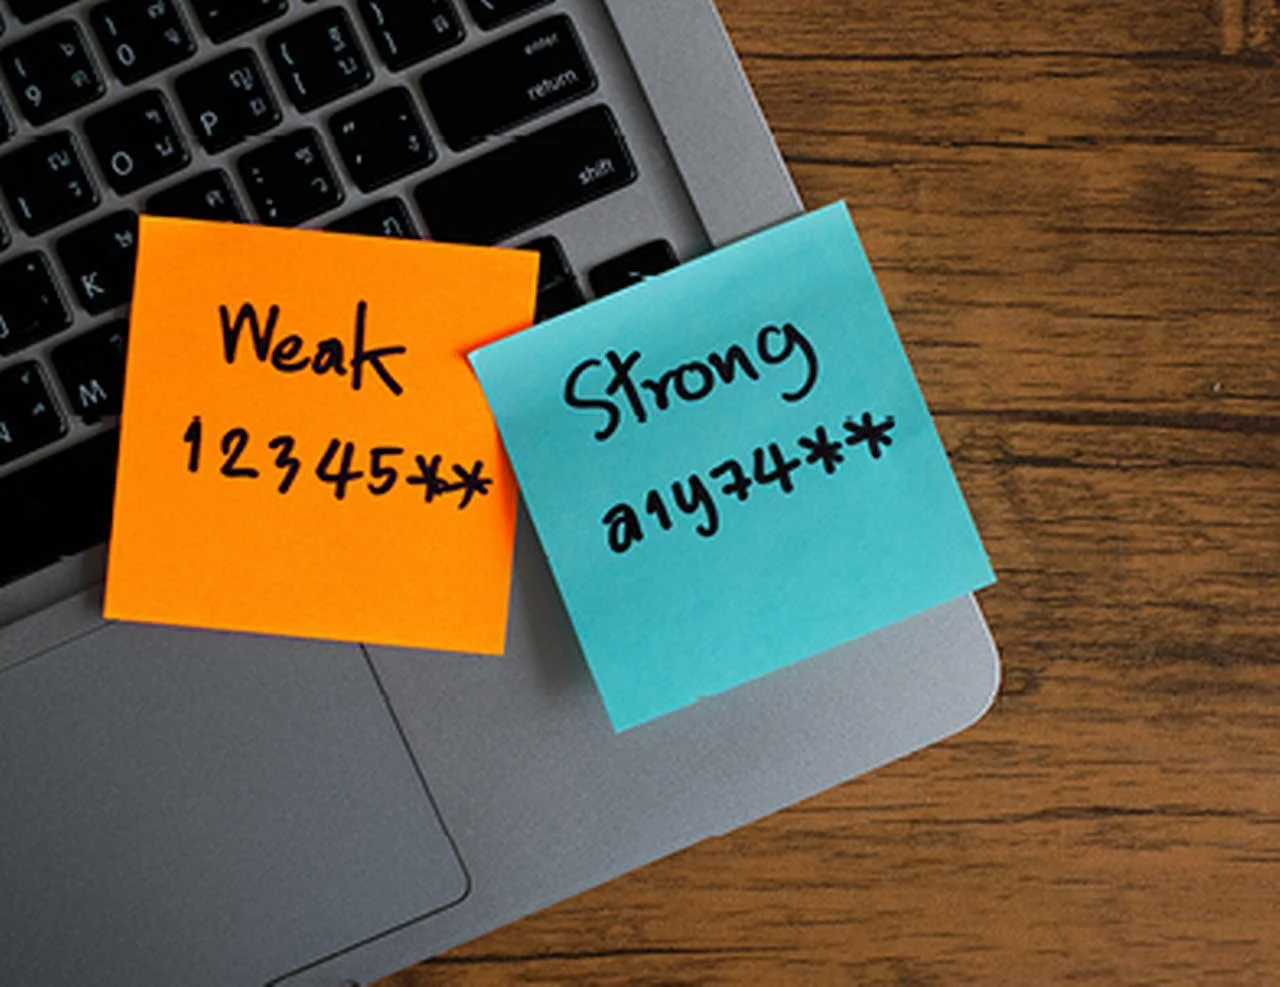
Disrupted operations, contractual liabilities, regulatory investigations and lasting reputational damage can all threaten long-term success. In many cases, attackers gain access through simple mistakes such as weak passwords or social engineering, phishing emails, unsecured remote access or employees inadvertently sharing sensitive information with unauthorized parties.
Your security is our priority, and we want to support you in strengthening your defenses. On this page, you will find practical guidance, expert insights and information to help your company stay more secure — whether you are a small enterprise or a global corporation.

Curious about your own security as a private person?
Because cyber risks don't stop at the office door: read more information about security topics relevant to private individuals.
Top 5 To-Dos for Corporations
In today’s digital landscape, cybersecurity is no longer an isolated technical issue that falls solely under the responsibility of the IT department. A comprehensive information security management system—requiring active participation and awareness from all employees—has become a critical success factor. Therefore, implementing and maintaining it should be a top priority on the executive agenda.

Promote a cultural shift
Engage your leadership team to actively advocate for cybersecurity.

Implement a Governance Framework
Define clear policies and procedures for data protection, financial transactions, and third-party partnerships.

Implement technology-based controls along the process chain
Ensure that all computers always have up-to-date antivirus software installed and that all necessary updates are consistently applied.

Strengthen the "human firewall" through training and awareness
Ensure employees can recognize and respond to phishing, social engineering, and other cyber threats.

Anticipate cyber threats & secure business continuity
Develop and regularly test incident response, crisis management, and recovery plans to minimize disruption and enable rapid restoration after a cyberattack.

Think twice before sharing your data
We will never ask you to disclose to us your access credentials (e.g. PIN, activation code, or initial access code/one-time code), whether we are engaging with you by email, text message, phone call, or in person. If you are asked for this information, end the communication immediately and contact us through a trusted channel to report the incident.
Key security topics for companies
Knowledge is the key to security – and we are here to guide you on this journey. Expand your knowledge of cybersecurity with our comprehensive knowledge bases.
Key topics
Detect & Remove Malware – Protection Against Malware
Malware
Detect & Remove Malware – Protection Against Malware
CEO fraud: Identify, prevent and act on boss fraud
CEO fraud
Identify, prevent and act on CEO fraud
Information Security & Email Protection Information Security
Information Security & Email Protection
Situational awareness & protection against unauthorized access Situational awareness
Situational awareness & protection against unauthorized access
AI & Deepfakes
Artificial intelligence AI (Artificial intelligence)

Cybercriminals increasingly use AI to make attacks more sophisticated, faster, and harder to detect. The dangers are diverse and often difficult to understand.
Deepfakes Deepfakes

AI can generate deceptively realistic voices, texts, images, and videos, for example, to impersonate a known person or spread false statements.
Enable your staff
Security incident or suspicious activity?
If you suspect unauthorized access, unusual account activity, or a cyber security incident involving your organization, please contact the responsible department within your company first.
If the incident relates to your Deutsche Bank accounts, services, or communications, our teams are here to support you.
- Contact your relationship manager directly, or
- Reach out to our security team:
Acting quickly can help protect your accounts and reduce potential impact.
If you suspect a cyber incident, unauthorized access, or a potential data compromise within your organization:
- Stop any suspicious activity or transactions immediately and alert the appropriate internal teams.
- Secure affected systems (for example, disconnect compromised devices from the network).
- Change access credentials (passwords, tokens, API keys) and enforce multi-factor authentication where applicable.
- Preserve relevant evidence (emails, logs, screenshots) to support investigation and remediation efforts.
- Inform internal stakeholders (IT, Compliance, Information Security, and Management) without delay.
- Contact your relationship manager or our security team (security.db@db.com) for immediate support in banking-related security incidents.
Depending on the nature and severity of the incident, you may also need to:
- Notify relevant regulators (for example, data protection authorities) within the timeframes required under applicable laws and regulations.
- Inform affected customers, partners, or other relevant stakeholders, if required by legal, regulatory, or contractual obligations.